Support
Fragmented IT across government levels, spread across central, state and PSU institutes, makes secure, consistent delivery of applications and data to employees difficult.
Fragmented IT across government levels, spread across central, state and PSU institutes, makes secure, consistent delivery of applications and data to employees difficult.
Compliance and data protection mandates require institutes to meet CERT-In and MeitY guidelines while safeguarding national data, defence IP and sensitive citizen records.
Budget constraints and a risk-averse, quick-ROI investment mindset limit IT capacity even as digitisation and e-governance demands grow, leaving valuable data increasingly vulnerable to cyber threats worldwide.


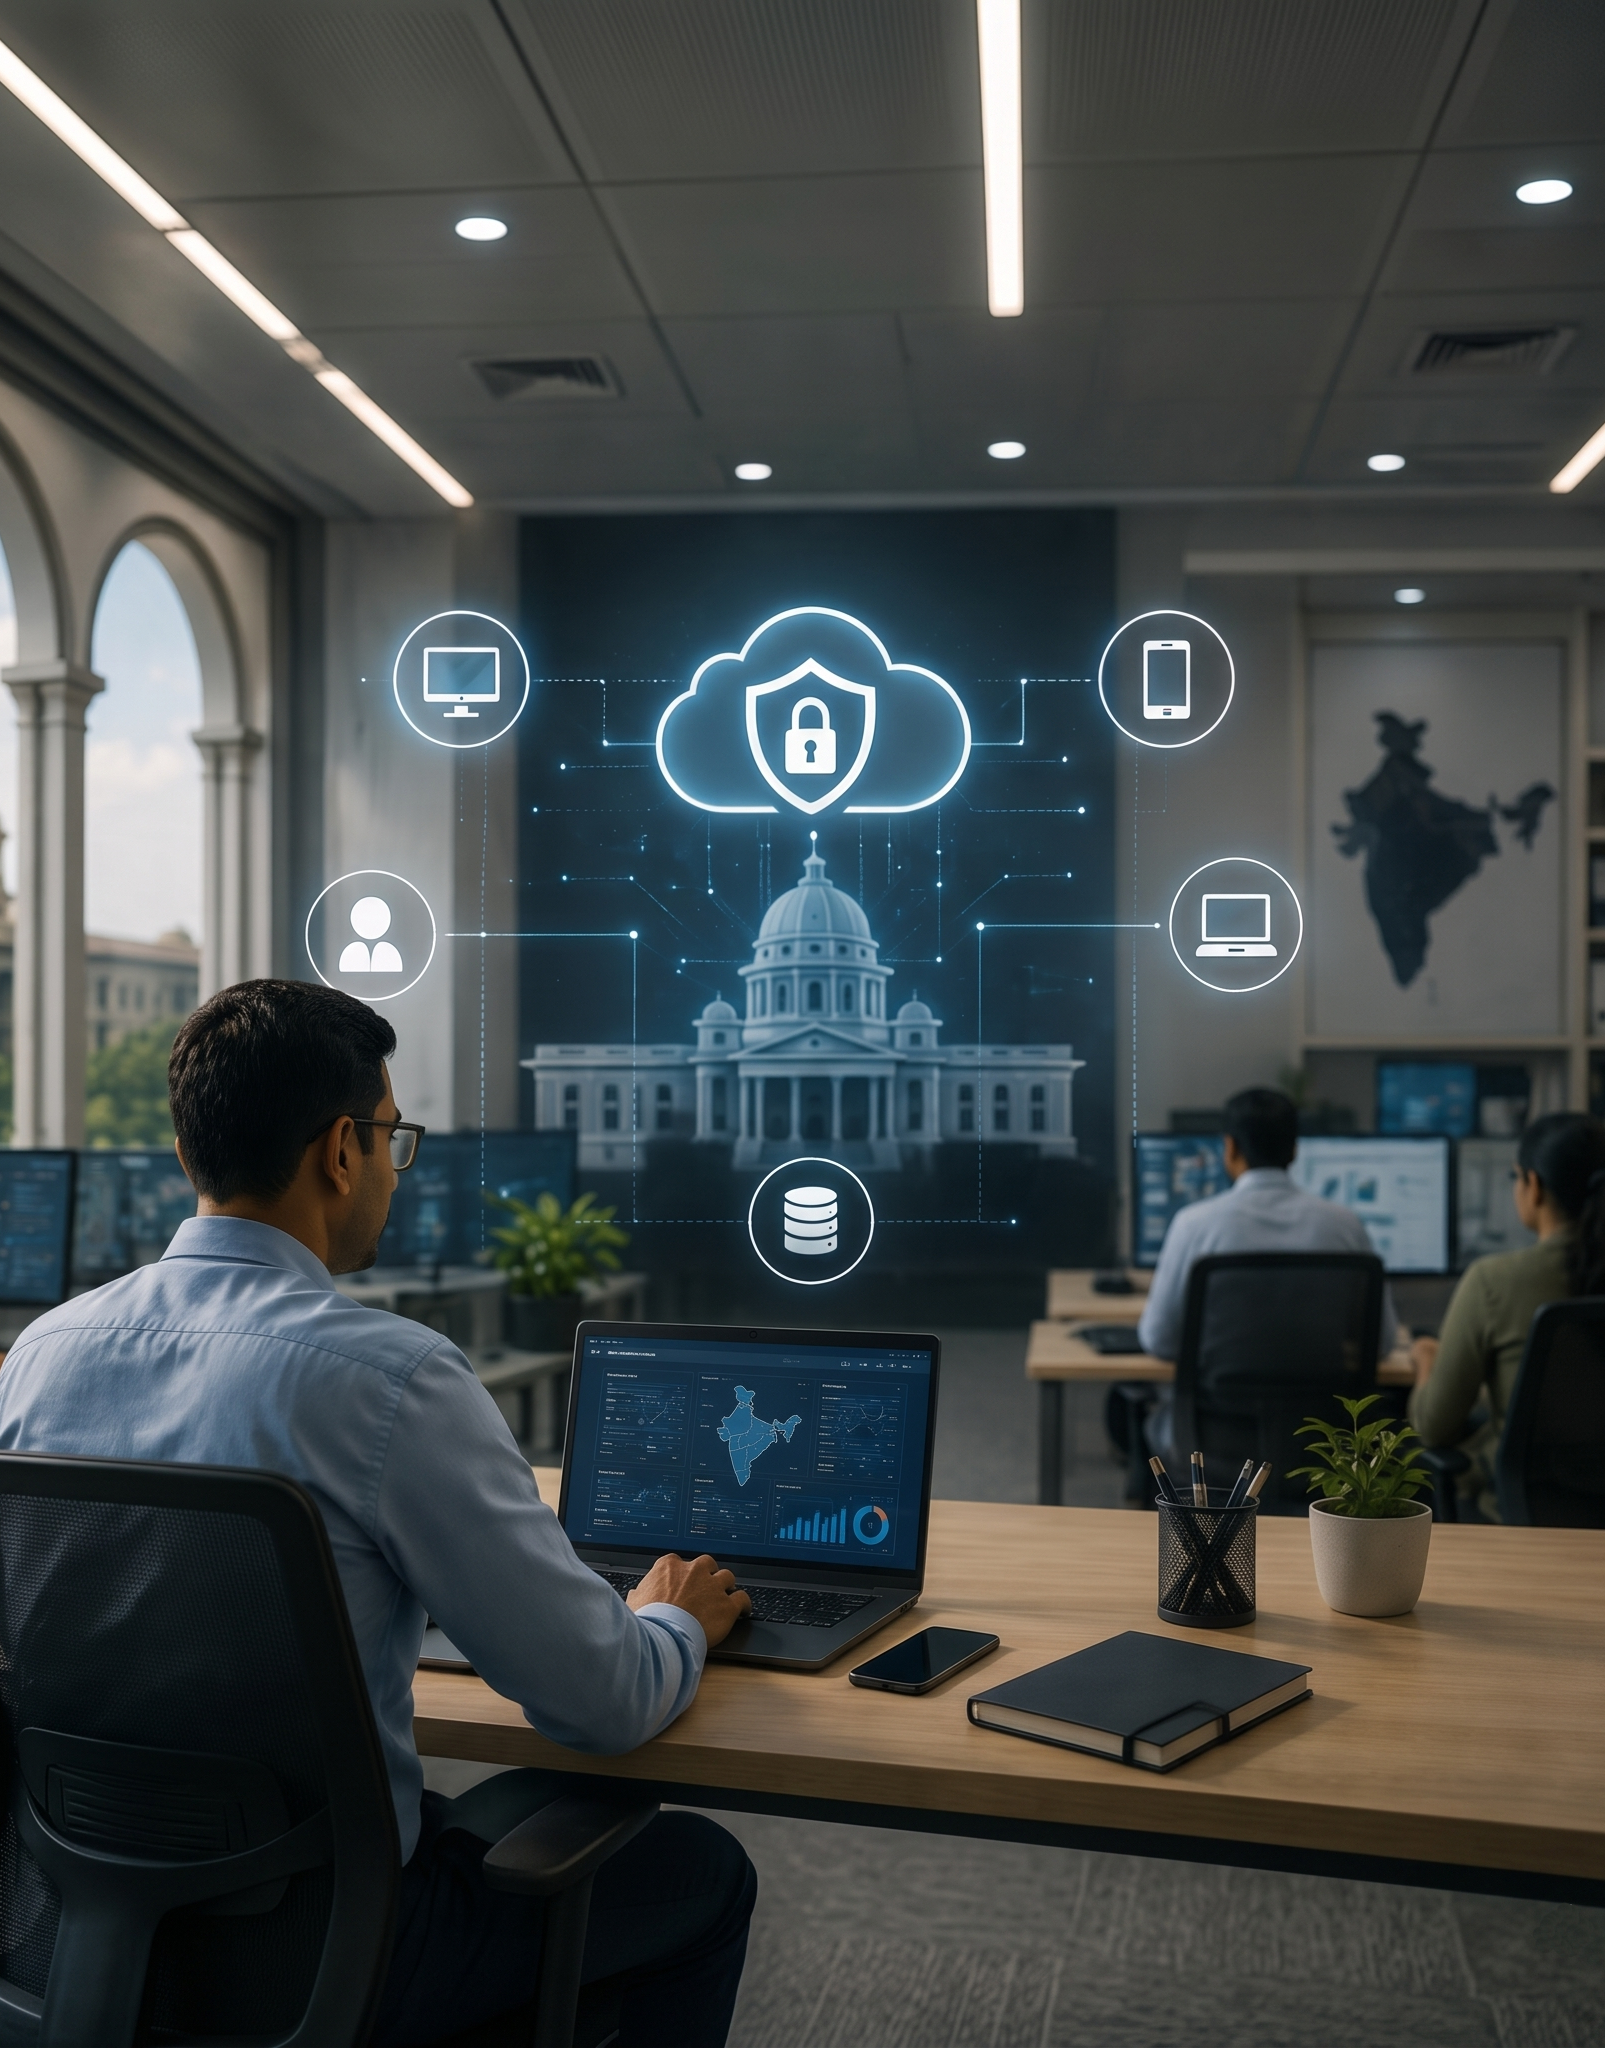
Consolidate applications and data in a centralised datacentre, isolate critical apps from devices and networks, and enable safe internet browsing to prevent cyberattacks.
Empower government employees, field officers and contract staff with anywhere, anytime access to mission-critical apps, eOffice, HRMS and internal portals, including from remote villages and talukas over low-bandwidth networks, using their own devices, thin clients or Accops Nano OS.
Replace PC-based computing with virtualisation, adopt low-configuration devices, cut endpoint security costs to about a fortieth, and upgrade seamlessly to newer Windows OS versions.
Avoid the time, effort and cost of extra infrastructure for third parties, letting vendors securely access systems from their own offices and devices.
Meet MeitY, CERT-In and DPDP Act requirements via contextual access and audit logs, blocking copy-paste, downloads and unauthorised USB use, and isolating workloads in air-gapped zones for data residency.